The chilling efficiency of nuclear missile systems, designed to deter or destroy, has long been a cornerstone of global security. These sophisticated arsenals, representing the apex of technological prowess and strategic planning, are intended to be impervious to compromise. Yet, beneath the veneer of unassailable strength, lies a complex ecosystem of hardware, software, and human interaction, all of which present potential avenues for exploitation. Uncovering vulnerabilities in nuclear missile systems is not merely an academic exercise; it is a critical undertaking that probes the very foundations of international stability and demands rigorous, ongoing scrutiny.
Modern nuclear missile systems are no longer isolated, mechanical behemoths. Instead, they are intricately woven into a vast network of interconnected systems, relying heavily on digital infrastructure for command, control, communication, and intelligence (C3I). This evolution, while enhancing operational flexibility and responsiveness, simultaneously introduces a new layer of susceptibility. The very technologies that enable rapid deployment and precise targeting also create pathways for malicious actors to probe, disrupt, or even commandeer these formidable weapons.
Software as a Critical Nexus
The software that governs every aspect of a nuclear missile system’s lifecycle – from design and production to deployment, launch, and deactivation – is a prime area of vulnerability. This includes operating systems, firmware, navigation algorithms, targeting software, and the code that facilitates communication between various components and command centers. Any flaw, bug, or backdoor within this digital architecture could have catastrophic consequences.
Legacy Code and Obsolete Architectures
A significant challenge lies in the longevity of many nuclear weapon systems. Developed during the Cold War, some systems still operate on or are supported by legacy code and hardware architectures. These older systems may lack the robust security features found in modern software and hardware, making them inherently more vulnerable to known exploits. Furthermore, the original developers may no longer be available, and documentation might be incomplete, making patching and updating these systems a complex and risky endeavor. The temptation to maintain operational capabilities with familiar, albeit outdated, technology can inadvertently create digital blind spots.
Supply Chain Integrity and Third-Party Dependencies
The development and maintenance of nuclear missile systems involve a vast supply chain, often encompassing numerous contractors and subcontractors. This extended network introduces risks related to the integrity of components and software provided by third parties. A compromised component, a subtly altered piece of firmware, or a malicious insertion into a software update at any stage of the supply chain could create a hidden vulnerability that remains undetected for years, waiting for exploitation. Ensuring the security and trustworthiness of every link in this chain is a monumental task.
Insider Threats and Human Error
While much attention is focused on external cyber threats, the human element remains a significant factor. Authorized personnel, whether through malicious intent or accidental actions, can introduce vulnerabilities. This could involve mishandling sensitive information, succumbing to social engineering attacks, or making errors during system operation or maintenance. The psychological pressures and the inherent complexity of operating such systems can contribute to an increased risk of human error.
Recent discussions surrounding the hidden vulnerabilities in nuclear missile systems have raised significant concerns about national security. An insightful article that delves deeper into this issue can be found at In The War Room, where experts analyze the potential risks and implications of outdated technology and insufficient cybersecurity measures in these critical defense systems. This exploration highlights the urgent need for modernization and comprehensive assessments to safeguard against potential threats.
The Hardware Backbone: A Tangible Point of Concern
While the digital realm often dominates discussions of cybersecurity, the physical hardware components of nuclear missile systems are equally susceptible to compromise. These are not just lines of code; they are tangible pieces of engineering, subject to physical tampering, environmental degradation, and design flaws that can be exploited.
Physical Tampering and Sabotage
The physical security of missile silos, launch control centers, and the missiles themselves is paramount. However, the sheer scale of these operations and the constant need for maintenance and upgrades present opportunities for unauthorized physical access. Sabotage, whether through direct damage or the introduction of compromised components, could render a system inoperable or, more chillingly, cause it to function in an unintended manner.
Access Control and Physical Security Measures
The effectiveness of physical security measures, including surveillance, access controls, and personnel vetting, is crucial. Any lapse in these protocols can create a window of opportunity for malicious actors. The challenge lies in maintaining the highest levels of vigilance across numerous geographically dispersed sites, often in remote and challenging environments.
Environmental Factors and Material Degradation
Nuclear missile systems are designed to withstand extreme conditions, but even the most robust hardware can degrade over time due to environmental factors such as temperature fluctuations, humidity, and radiation. Material fatigue, corrosion, and other forms of degradation can lead to unexpected system failures or create physical weaknesses that could be exploited. Regular inspections and maintenance are essential, but the sheer number of components and the complexity of the systems make comprehensive monitoring a constant challenge.
Electromagnetic Interference and Jamming
Modern electronic systems are susceptible to electromagnetic interference (EMI) and jamming. Nuclear missile systems rely on precise communication and signal reception. External sources of strong electromagnetic radiation, whether intentional jamming or accidental interference, could disrupt guidance systems, communication links, or the activation sequences of a missile.
Signal Integrity and Redundancy
Ensuring the integrity of signals is vital. Redundant communication channels and sophisticated signal processing techniques are employed to mitigate these risks, but the increasing prevalence of advanced jamming technologies poses an ongoing threat. The ability to disrupt or spoof critical signals could have severe implications for command and control.
Command and Control: The Brains of the Operation and Their Vulnerabilities
The command and control (C2) systems for nuclear missile forces are the ultimate arbiters of their use. These systems are designed for ultimate reliability and security, but they are also complex human-machine interfaces that are inherently prone to certain vulnerabilities. The decision-making process, the transmission of launch orders, and the verification of those orders all represent critical junctures where vulnerabilities could be exploited.
Authentication and Authorization Protocols
The systems that authenticate and authorize the launch of nuclear missiles are designed with multiple layers of security. However, the human element in these protocols is always a factor. Sophisticated social engineering, insider collusion, or the compromise of authentication credentials could potentially lead to unauthorized access or the transmission of false orders.
Multi-Factor Authentication and Biometrics
The implementation and robustness of multi-factor authentication and the potential use of biometric identifiers are key considerations. While these technologies enhance security, they are not infallible and can themselves be subject to circumvention or compromise under certain circumstances.
Communication Channels and Encryption
The communication channels used to transmit launch orders are heavily encrypted and protected. However, the theoretical possibility of breaking advanced encryption algorithms, or the compromise of encryption keys, remains a concern. Furthermore, the physical security of the communication infrastructure itself is crucial to prevent interception or manipulation.
The Human Factor in Decision-Making
The human operators of C2 systems are trained to follow strict protocols, but the psychological pressures of a high-stakes environment, coupled with the potential for deception or misdirection, can introduce vulnerabilities. The Chain of Custody for launch orders and the integrity of verification processes are critical to prevent accidental or coerced launches.
Decision Support Systems and Automation
While automation can reduce human error in some contexts, it can also introduce new vulnerabilities if the underlying algorithms are flawed or if the system is manipulated. The reliance on automated decision support systems needs careful consideration to ensure that they do not create single points of failure or introduce unforeseen biases.
Testing and Evaluation: A Double-Edged Sword
The process of testing and evaluating nuclear missile systems is essential for identifying and mitigating vulnerabilities. However, the very act of testing can, if not conducted with the utmost discretion and security, inadvertently reveal weaknesses or create new ones.
Penetration Testing and Red Teaming
Regular penetration testing and red teaming exercises are crucial for simulating real-world attacks and identifying potential weaknesses. These exercises involve authorized teams attempting to breach the defenses of the missile systems, mimicking the tactics and techniques of potential adversaries.
The Risk of Revealing Exploits
While invaluable, these tests must be conducted in highly controlled environments. If sensitive information about discovered vulnerabilities or successful exploitation techniques were to leak, it could provide adversaries with a roadmap for attack. The careful management of findings and the swift remediation of identified issues are paramount.
Vulnerability Disclosure Programs and Information Sharing
The concept of responsible vulnerability disclosure, where researchers report their findings to the system operators rather than publicly disclosing them, is gaining traction in various sectors. For nuclear missile systems, however, the stakes are astronomically high. The mechanisms for securely reporting and addressing such disclosures are critical.
The Challenge of External Reporting
Encouraging external researchers to report potential vulnerabilities in highly classified systems is a complex challenge. The legal and security ramifications for individuals who discover such flaws can be daunting. Establishing secure and anonymous channels for reporting is vital, alongside clear protocols for evaluation and response.
Recent discussions have highlighted a concerning article that delves into hidden vulnerabilities in nuclear missile systems, raising alarms about the potential risks associated with outdated technology and insufficient cybersecurity measures. As nations continue to modernize their defense strategies, it becomes increasingly crucial to address these overlooked weaknesses to ensure global security and prevent catastrophic failures.
The Evolving Landscape of Threat and Defense
| Metric | Description | Potential Impact | Example Vulnerability | Mitigation Strategy |
|---|---|---|---|---|
| Software Exploits | Flaws in missile guidance or control software | Unauthorized missile launch or failure to launch | Buffer overflow in missile control firmware | Regular code audits and secure coding practices |
| Communication Interception | Interception or jamming of command signals | Loss of command and control, false commands | Unencrypted command transmission | Use of encrypted and authenticated communication channels |
| Insider Threats | Malicious actions by authorized personnel | Sabotage or unauthorized launch | Compromised launch codes | Strict access controls and personnel vetting |
| Hardware Tampering | Physical modification or insertion of malicious components | System malfunction or backdoor access | Insertion of rogue chips in missile electronics | Regular hardware inspections and supply chain security |
| Legacy System Vulnerabilities | Outdated technology with known security flaws | Exploitation by cyber attackers | Unpatched operating systems in control centers | System upgrades and patch management |
The pursuit of uncovering vulnerabilities in nuclear missile systems is not a static endeavor; it is a perpetual arms race against constantly evolving threats. As defensive measures become more sophisticated, so too do the methods employed by potential adversaries to circumvent them.
The Rise of Artificial Intelligence and Machine Learning
The increasing integration of artificial intelligence (AI) and machine learning (ML) into both offensive and defensive cyber capabilities presents a new frontier. AI-powered tools can be used to probe systems for weaknesses, automate the process of exploiting vulnerabilities, and adapt to defensive measures in real-time.
AI-Driven Attacks and Countermeasures
The development of AI-driven offensive capabilities raises concerns about the potential for increasingly sophisticated and rapid attacks. Conversely, AI can also be employed in defensive systems to detect anomalous behavior, predict potential threats, and automate responses. The balance between these AI applications is a critical area of focus.
Space-Based Threats and Electronic Warfare
The increasing reliance on space-based assets for communication, navigation, and intelligence gathering means that these assets are also potential targets. Attacks on satellites or the jamming of signals used for missile guidance could have profound implications. The development of space-based electronic warfare capabilities further complicates this threat landscape.
Protecting Critical Space Infrastructure
Ensuring the resilience and security of the space-based infrastructure that supports nuclear missile systems is as important as securing the terrestrial components. This involves developing countermeasures against jamming, spoofing, and physical attacks on satellites.
The Importance of Continuous Monitoring and Adaptation
The dynamic nature of cyber threats necessitates a paradigm of continuous monitoring and adaptation. Static security measures, once implemented, will inevitably become outdated. Nuclear missile systems require a robust, real-time security posture that can detect emerging threats and rapidly deploy countermeasures.
Proactive Threat Hunting and Intelligence
Moving beyond reactive defense, a proactive approach involving threat hunting – actively searching for signs of compromise – and intelligence gathering about emerging adversary capabilities is essential. This allows for the anticipation of future threats and the development of preventative strategies.
In conclusion, uncovering vulnerabilities in nuclear missile systems is a multifaceted and ongoing challenge that requires a comprehensive understanding of the intricate interplay between hardware, software, human factors, and the ever-evolving threat landscape. It is a testament to the dedication of security professionals worldwide that these systems, despite their inherent complexities and potential for exploitation, have maintained a remarkable record of stability. However, complacency is the greatest vulnerability of all. The continuous pursuit of knowledge, rigorous testing, and a steadfast commitment to adaptation are essential to ensuring that these powerful weapons remain a deterrent, and never a tool of irreversible destruction. The silence of the silo must be a testament to robust security, not an ominous precursor to a catastrophic failure.
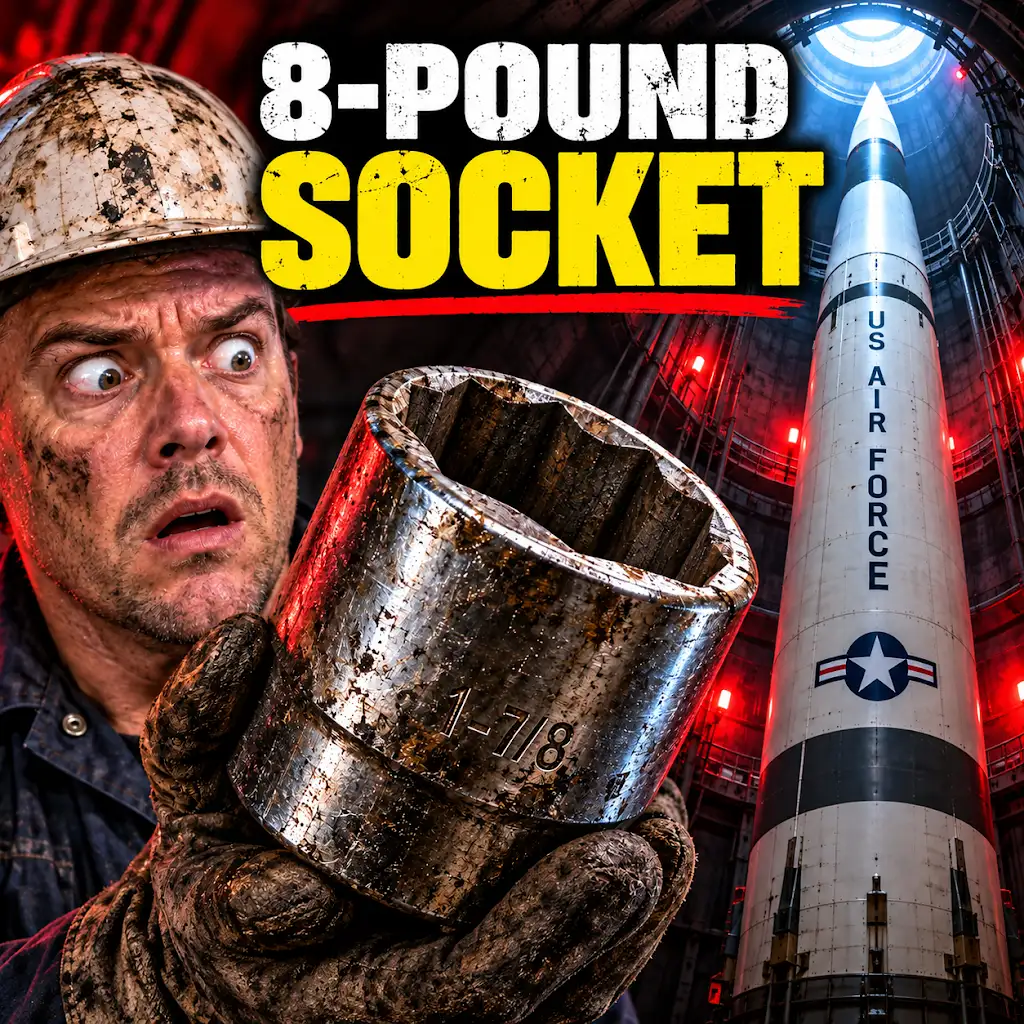
How a Dropped Socket Destroyed a Titan II Missile
FAQs
What is the hidden vulnerability in nuclear missile systems?
The hidden vulnerability in nuclear missile systems refers to a flaw or weakness in the system that could potentially be exploited by hackers or malicious actors to gain unauthorized access or control over the missiles.
How was the hidden vulnerability discovered?
The hidden vulnerability in nuclear missile systems was discovered by a team of researchers who conducted a thorough analysis of the systems’ software and hardware components. They identified a specific weakness that could be exploited to compromise the security of the systems.
What are the potential consequences of the hidden vulnerability in nuclear missile systems?
The potential consequences of the hidden vulnerability in nuclear missile systems are severe and could include unauthorized launch of missiles, tampering with missile trajectories, or even disabling the systems altogether. These consequences could have catastrophic effects on national security and global stability.
What steps are being taken to address the hidden vulnerability in nuclear missile systems?
Upon discovery of the hidden vulnerability, the researchers who identified it have alerted the relevant authorities and manufacturers of the nuclear missile systems. They are working together to develop and implement patches or updates to fix the vulnerability and enhance the security of the systems.
How can the public stay informed about the progress in addressing the hidden vulnerability in nuclear missile systems?
The public can stay informed about the progress in addressing the hidden vulnerability in nuclear missile systems by following updates from reputable news sources, government agencies, and cybersecurity organizations. It is important to stay informed and aware of any developments regarding the security of nuclear missile systems.