Nuclear weapons engineering, a field defined by its pursuit of unimaginable power and the paramount importance of safety, has not been without its share of near misses and outright failures. These incidents, though often shrouded in secrecy, offer invaluable lessons that have shaped the design, maintenance, and operational protocols of these potent arsenals. Examining these engineering missteps reveals a persistent tension between the complex theoretical underpinnings of nuclear weapon functionality and the unforgiving realities of material science, human error, and environmental factors. The history of nuclear weapons development is, in many ways, a history of overcoming these engineering challenges, with each failure serving as a stark reminder of the stakes involved.
The earliest days of nuclear weapons engineering were characterized by a frantic race against time and an incomplete understanding of the fundamental physics involved. The Manhattan Project, while a monumental scientific and engineering achievement, was also a crucible where theoretical concepts were being translated into tangible, and potentially catastrophic, devices for the first time. This unprecedented undertaking inevitably led to unforeseen design challenges and material limitations.
Material Science and Criticality Control
One of the most fundamental challenges in designing a nuclear weapon is achieving and controlling criticality – the point at which a nuclear chain reaction becomes self-sustaining. Early designs, particularly for the plutonium-based “Fat Man” bomb used at Nagasaki, involved complex implosion mechanisms. The precise shaping and detonation of high explosives were critical to compressing the fissile material (plutonium-239) into a supercritical mass.
- The Implosion Lens Problem: The original designs for the explosive lenses used in implosion weapons were imperfect. These lenses, shaped to focus the blast wave uniformly, relied on the precise composition and detonation timing of different high-explosive materials. Inadequate understanding of the detonation wave propagation and the potential for asymmetry in the explosive charge led to early tests demonstrating uneven compression. This could result in a “fizzle” – a partial nuclear reaction that releases energy but not the intended explosive yield, or worse, a dispersal of the fissile material without detonation. The successful implosion required incredibly precise manufacturing tolerances, which were difficult to achieve with the technology of the time.
- Plutonium Handling and Stability: Plutonium-239, a key fissile material, presents unique engineering challenges. It exists in several different allotropes (crystal structures) that change with temperature. These phase transitions can cause dimensional instability, making it difficult to maintain the precise geometry required for critical assembly. Early engineers had to contend with the fact that plutonium could swell or shrink, potentially leading to a premature or delayed reaction, or even preventing criticality altogether. The alpha phase, which is stable at room temperature, is particularly problematic due to its tendency to expand. Alloying plutonium with other elements, such as gallium, was a crucial engineering solution to stabilize it in the desired delta phase, but this itself was a discovery born from understanding early material instability issues.
- The “Tickling the Dragon’s Tail” Accidents: The accidents involving Louis Slotin and Harry Daghlian in 1945 and 1946, respectively, are stark reminders of the dangers of handling fissile material outside of controlled weapon designs. Slotin was conducting experiments to determine the critical mass of a subcritical assembly of plutonium spheres, using a screwdriver to keep them slightly separated. The screwdriver slipped, allowing the hemispheres to touch and the assembly to go prompt critical. While Slotin was able to quickly separate the hemispheres, he received a lethal dose of radiation. Daghlian had a similar accident while experimenting with a plutonium core and a neutron-reflecting tungsten carbide brick. These incidents, though not weapon failures in the sense of a detonated device, highlighted the extreme sensitivity of fissile materials and the profound risks associated with manual handling and inadequate safety protocols during the engineering and testing phases.
One notable article that discusses engineering failures in nuclear weapons systems can be found on In The War Room. This piece delves into various historical incidents where design flaws and technical malfunctions have led to significant risks and challenges in maintaining nuclear arsenals. For more insights on this critical topic, you can read the article here: Engineering Failures in Nuclear Weapons Systems.
Design Simplification and the Quest for Reliability: Lessons from Early Weapon Systems
As the understanding of nuclear physics and engineering advanced, the focus shifted towards developing more reliable and deployable weapon systems. This involved streamlining designs, incorporating safety mechanisms, and learning from the initial complexities and vulnerabilities of early prototypes.
The Evolution of the Triggering Mechanism
The complex implosion mechanisms of early bombs, while effective, were intricate and prone to failure. The development of simpler, more robust triggering mechanisms became a priority.
- Gun-Type Assembly: The “Little Boy” bomb dropped on Hiroshima, a uranium-based weapon, utilized a simpler gun-type assembly. In this design, a subcritical mass of enriched uranium is fired down a barrel into another subcritical mass, forming a supercritical assembly. While conceptually simpler than implosion, this design was only suitable for uranium-235 due to its lower spontaneous fission rate. Plutonium-239’s higher spontaneous fission rate would cause it to detonate prematurely in a gun-type design before the full assembly could be achieved, leading to a fizzle. The successful development of the gun-type mechanism was a significant engineering feat, but its limitations in fissile material choice underscored the need for different approaches.
- The Importance of Nuclear “Maturity”: Early weapon designs, particularly those relying on implosion, required a certain degree of “maturity” in the nuclear material – meaning that the fissile material had undergone sufficient neutron bombardment to produce a specific isotopic composition. However, the rapid production of weapons meant that materials might not have reached this ideal state. This could lead to variations in performance and potential engineering challenges related to unpredictable neutron emission rates. Engineers had to account for these variations to ensure consistent yields.
- The “Reliability” Debate in Early Testing: Initial nuclear tests often aimed to demonstrate the functionality and yield of newly designed weapons. However, the results of these tests were not always as predicted. Discrepancies between calculated and observed yields pointed to shortcomings in the theoretical models and the engineering execution. For example, some early tests might have produced yields lower than expected due to inefficiencies in the implosion process or incomplete fission of the available fissile material. This led to a continuous cycle of design refinement and further testing to improve reliability.
Environmental Factors and Extreme Conditions: The Challenges of Deployment
Nuclear weapons are designed to function in a wide range of environments, from the frigid Arctic to the harsh deserts. This necessitates engineering solutions that account for extreme temperatures, humidity, shock, vibration, and electromagnetic interference. Failures in understanding or mitigating these environmental impacts can lead to catastrophic consequences.
Temperature Extremes and Material Degradation
The performance of nuclear weapons is highly dependent on the integrity of their components, many of which are susceptible to temperature fluctuations.
- High-Explosive Aging and Sensitivity: The high explosives used in implosion devices are sensitive to temperature. Prolonged exposure to high temperatures can lead to aging and desensitization, meaning the explosives may not detonate with the required speed and uniformity. Conversely, extreme cold can make them brittle and more prone to accidental detonation from shock. The engineering challenge lies in developing explosives that remain stable and predictable across a wide operational temperature range, and in designing casings and storage systems that mitigate extreme temperature exposure.
- Electronic Component Reliability: Modern nuclear weapons contain sophisticated electronic components for detonation, arming, and safety interlocks. These components, like any electronics, are susceptible to extreme temperatures. High temperatures can cause circuit boards to warp, solder joints to weaken, and semiconductors to fail. Low temperatures can reduce battery performance and affect the function of liquid crystal displays or other temperature-sensitive interfaces. Extensive testing and the use of specialized, radiation-hardened and temperature-resistant electronics are crucial engineering solutions to this problem.
- The “Cold War” Storage Dilemma: During the Cold War, vast quantities of nuclear weapons were stored for extended periods, often in harsh climates. Ensuring the long-term reliability of these weapons under such conditions was a significant engineering undertaking. This included developing specialized containers, environmental control systems, and rigorous maintenance schedules to prevent degradation of materials and components.
Shock, Vibration, and Accidental Detonation Risks
Nuclear weapons are designed to withstand significant shock and vibration during transport and potential accidental drops, yet they must also detonate reliably when commanded. This presents a delicate engineering balance.
- The “Broken Arrow” Incidents: While not always directly linked to engineering failures in the sense of a device malfunctioning to detonate, “Broken Arrow” incidents – accidents involving nuclear weapons – highlight the critical importance of robust engineering for preventing unintended detonation. Accidents involving aircraft crashes, train derailments, or naval collisions have, on rare occasions, led to the dispersal of nuclear material or the accidental arming of a weapon. The engineering goal is to ensure that even in extreme accident scenarios, the nuclear explosive components remain inert and incapable of initiating a nuclear detonation.
- The Design of Safe and Arming Mechanisms: Modern nuclear weapons incorporate multiple safety features designed to prevent accidental detonation. These include Permissive Action Links (PALs), which require a specific code to arm the weapon, and environmental sensors that prevent arming in unauthorized conditions. The engineering of these systems must be exceptionally robust, ensuring they function correctly and cannot be bypassed inadvertently or by enemy action. Failures in these safety mechanisms, even in a non-nuclear context, can have devastating consequences.
- The Impact of Transport and Handling: The stresses experienced during the transport of nuclear weapons – whether by road, rail, air, or sea – can be significant. Engineering designs must incorporate shock absorbers, vibration dampeners, and secure locking mechanisms to protect the weapon’s internal components. Failures in these protective measures could lead to damage that compromises the weapon’s reliability or, in the worst-case scenario, increases the risk of accidental initiation.
Human Error and Procedural Lapses: The Unpredictable Variable
Despite the most sophisticated engineering and safety protocols, the human element remains a critical factor in the safe operation and maintenance of nuclear weapons. Errors in judgment, misinterpretation of procedures, or simple oversight can have profound implications.
Maintenance and Servicing Errors
The complex nature of nuclear weapons requires highly skilled personnel and meticulous adherence to detailed maintenance procedures.
- The “Palomares” and “Thule” Air Disaster Accidents: The accidental mid-air collision of a B-52 bomber with a KC-135 refueling tanker over Palomares, Spain, in 1966, and a similar incident involving a B-52 over Thule, Greenland, in 1968, resulted in the loss of nuclear weapons. In both cases, the conventional explosives within the nuclear bombs detonated due to the impact, dispersing radioactive plutonium over large areas. While the nuclear devices themselves did not detonate, these accidents highlight the catastrophic potential when the safety systems fail under extreme stress, and the importance of preventing accidental detonation of the high explosives. Investigations revealed human factors, including procedural deviations and inadequate training, contributed to the severity of these events.
- Improper Assembly or Disassembly: During maintenance or repair, errors in the assembly or disassembly of components can lead to compromised safety or operational failures. This could range from incorrectly installing a vital safety interlock to misaligning critical parts within the detonation system. Rigorous checklists, redundant verification steps, and continuous training are essential to mitigate these risks.
- Cross-Contamination and Contamination Control: In any complex engineering system, there is a risk of contamination. In the context of nuclear weapons, this can involve radioactive contamination of non-nuclear components or vice-versa. Strict protocols for handling and decontamination are crucial, and failures in these procedures can lead to compromised weapon integrity or pose health risks to personnel.
Launch and Arming Sequence Errors
The procedures for launching and arming nuclear weapons are multi-layered and require precise execution.
- The “False Alarm” Incidents: Throughout the Cold War, there were several instances where early warning systems mistakenly indicated an incoming Soviet missile attack, leading to moments of extreme tension where launch procedures could have been initiated. While none of these resulted in an actual launch, they underscore the critical importance of robust and reliable warning systems and the human element in decision-making. Engineering plays a role in designing systems that are resistant to false positives and in providing clear, unambiguous information to decision-makers.
- Procedural Deviations during Exercises: Even during training exercises, deviations from established procedures can occur. These might involve skipping a step, performing a step out of order, or misinterpreting an instruction. While designed to simulate real-world scenarios, these deviations can reveal vulnerabilities in the procedures themselves or in the training provided. Lessons learned from such deviations lead to refinements in both the procedures and the training.
- Communication Breakdowns: Effective communication is paramount in all stages of nuclear weapon operations. Failures in communication, whether due to technical issues or human error, can lead to misunderstandings, delays, or incorrect actions. Engineering aims to provide reliable communication systems, while training emphasizes clear and concise communication protocols.
Engineering failures in nuclear weapons systems can have catastrophic consequences, as highlighted in a related article that discusses various incidents and their implications for national security. The article emphasizes the importance of rigorous testing and oversight to prevent such failures from occurring. For a deeper understanding of these critical issues, you can read more in this insightful piece found at this link.
The Legacy of Near Misses and Continuous Improvement: Enduring Lessons
| Metric | Description | Example/Value | Impact |
|---|---|---|---|
| Failure Rate | Percentage of nuclear weapons systems that experience engineering failures | 0.01% – 0.1% | Potential accidental detonation or failure to detonate |
| Mean Time Between Failures (MTBF) | Average operational time between failures in nuclear weapons components | 10,000 – 100,000 hours | Reliability assessment for maintenance scheduling |
| False Positive Rate | Rate at which systems incorrectly detect threats or trigger alarms | Less than 0.001% | Risk of accidental launch or unnecessary alerts |
| Component Degradation Rate | Rate at which critical components lose functionality over time | 1-2% per year | Need for refurbishment or replacement |
| System Redundancy Level | Number of backup systems to prevent failure | 3-5 redundant systems | Increases overall system reliability and safety |
| Human Error Incidence | Frequency of engineering failures caused by human mistakes | Approximately 10-15% of failures | Highlights need for training and procedural improvements |
| Environmental Stress Impact | Effect of environmental factors (temperature, radiation) on system failure | Up to 5% increase in failure rate under extreme conditions | Necessitates robust design and testing |
The history of nuclear weapons engineering is replete with near misses, incidents that could have had catastrophic consequences but were averted through a combination of luck, quick thinking, and the inherent robustness of some of the engineered systems. These events serve as powerful catalysts for continuous improvement.
The Importance of “Defense in Depth”
The concept of “defense in depth” is central to nuclear weapons safety and security engineering. It means implementing multiple, independent layers of protection so that the failure of one layer does not lead to disaster.
- Redundancy in Safety Systems: Nuclear weapons are designed with redundant safety systems. For example, there might be multiple independent mechanisms to prevent accidental detonation, or multiple sensors to confirm the correct environmental conditions for arming. If one system fails, the others are intended to maintain safety. Engineering failures in one component are thus mitigated by the presence of other functioning components.
- Physical Security Measures: Beyond the weapon itself, physical security measures are crucial to prevent unauthorized access or tampering. This includes secure storage facilities, armed guards, and surveillance systems. Failures in these security layers can create opportunities for sabotage or theft, underscoring the need for robust engineering of both the weapon and its surrounding infrastructure.
- The Role of Independent Verification: Independent verification and oversight are critical throughout the lifecycle of a nuclear weapon. This involves review by different teams, external agencies, and regulatory bodies to ensure that designs, manufacturing processes, and operational procedures meet stringent safety and security standards. Engineering challenges are identified and addressed through this rigorous process of scrutiny.
The Impact of Secrecy on Learning
The inherent secrecy surrounding nuclear weapons programs presents a unique challenge to the learning process. While necessary for national security, it can also hinder the open sharing of lessons learned from failures and near misses.
- Limited Dissemination of Knowledge: While internal lessons are learned within specific programs or nations, the broader international community may not benefit from these insights. This can lead to the repetition of similar mistakes or a slower pace of overall progress in nuclear safety.
- The Role of “Near Miss” Reporting: Countries with nuclear weapons programs often have internal mechanisms for reporting and investigating “near miss” incidents. The insights gained from these investigations, even if not publicly disclosed, contribute to the iterative improvement of designs and procedures.
- International Cooperation in Non-Proliferation: While direct sharing of weapon design information is not possible, international cooperation on non-proliferation efforts and the development of safety standards for nuclear materials in civilian applications can indirectly benefit from lessons learned in the nuclear weapons realm. The underlying principles of material handling, containment, and safety system design are often transferable.
In conclusion, the engineering of nuclear weapons, by its very nature, is a field where failures carry immense weight. From the initial theoretical hurdles of achieving criticality to the practical challenges of ensuring reliability in extreme environments and preventing human error, each setback has contributed to a deeper understanding and a more robust approach to safety. The lessons learned from material science limitations, triggering mechanism complexities, environmental stresses, and the ever-present human factor have not only shaped the design and maintenance of existing arsenals but also informed the ongoing global discourse on nuclear disarmament and non-proliferation. The persistent pursuit of engineering excellence, driven by the stark lessons of past near misses, remains the bedrock of ensuring that the unimaginable power of nuclear weapons is never unleashed in error or by design.
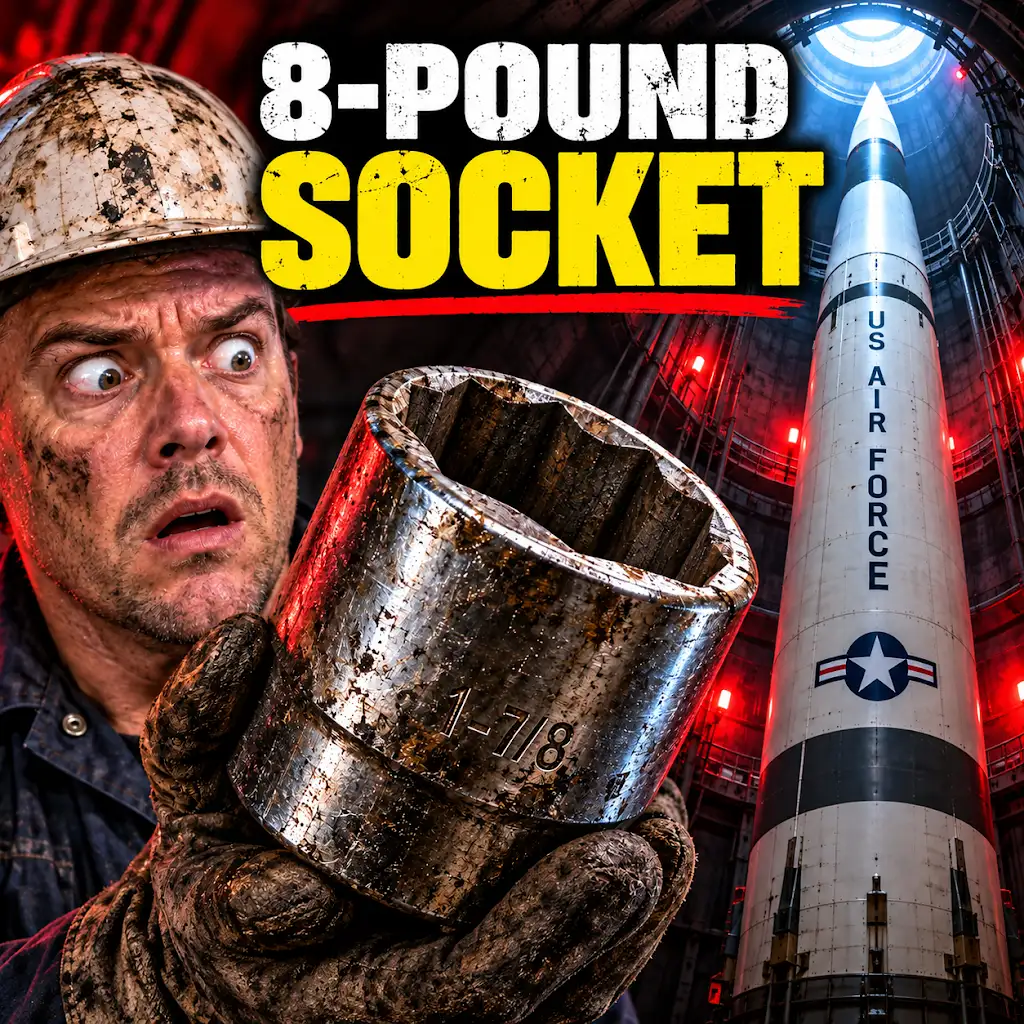
How a Dropped Socket Destroyed a Titan II Missile
FAQs
What is an engineering failure in nuclear weapons systems?
An engineering failure in nuclear weapons systems refers to a malfunction, error, or flaw in the design, construction, or operation of components within a nuclear weapon system that could potentially lead to a catastrophic event.
What are some examples of engineering failures in nuclear weapons systems?
Examples of engineering failures in nuclear weapons systems include issues with safety mechanisms, control systems, detonation mechanisms, and overall system reliability. These failures can result in accidental detonation, unauthorized access, or other dangerous situations.
How do engineering failures in nuclear weapons systems impact safety and security?
Engineering failures in nuclear weapons systems can compromise safety and security by increasing the risk of accidental detonation, unauthorized use, or loss of control over the weapons. These failures can have devastating consequences for both the individuals involved and the surrounding environment.
What measures are in place to prevent engineering failures in nuclear weapons systems?
To prevent engineering failures in nuclear weapons systems, rigorous testing, quality control procedures, and maintenance protocols are implemented. Additionally, strict security measures, training programs, and regular inspections are put in place to ensure the safe and reliable operation of these systems.
What are the potential consequences of an engineering failure in nuclear weapons systems?
The potential consequences of an engineering failure in nuclear weapons systems are severe and can include accidental detonation, radioactive contamination, loss of life, environmental damage, and international security threats. It is crucial to address and mitigate any engineering failures promptly to prevent such catastrophic outcomes.